Most companies don't decide to change how IT gets handled. They accumulate reasons until something forces it.
That's not a criticism — it's how operational decisions actually get made when the current arrangement mostly works. The problem is that the forcing event is usually expensive, and by the time it arrives, the reasons have been visible for a couple of years.
Here are seven of them. Some are specific enough to check this afternoon.
This is the most checkable item on the list, so start here.
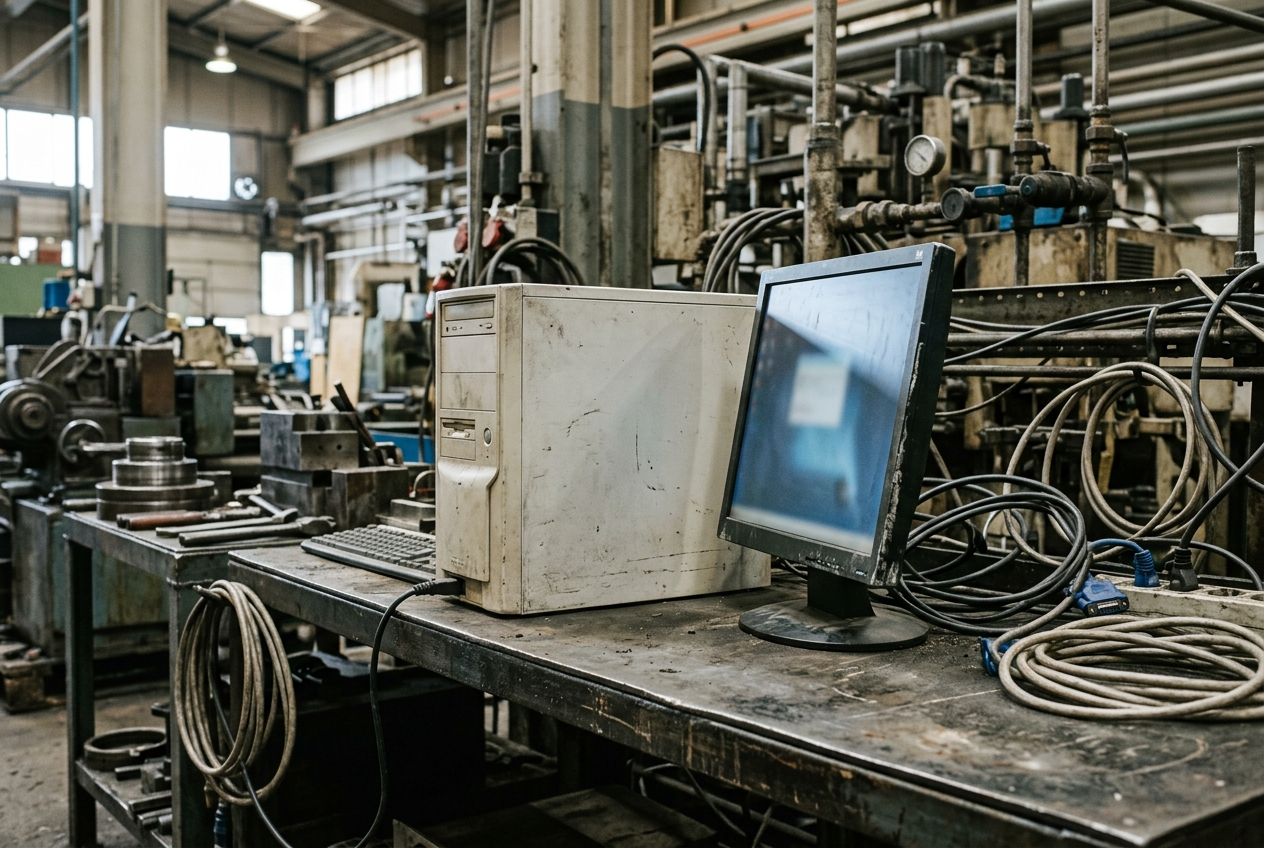
Windows 10 reached end of support on October 14, 2025. Microsoft's own language is unambiguous: technical assistance, feature updates, and security updates are no longer provided.
Nearly a year later, Statcounter measured Windows 10 at 23.67% of US desktop Windows in August 2026 — roughly one machine in four, still running, still unpatched unless someone bought coverage.
There is coverage available, and this is where it gets expensive. Microsoft's Extended Security Updates program for organizations costs $61 per device for year one, $122 for year two, and $244 for year three, up to three years. Two things about that pricing that catch people out:
And a correction worth making, because a lot of content gets it wrong: the $30 consumer ESU option — and the free path through Windows Backup — is not available for business machines. Microsoft is categorical about it: devices joined to an Active Directory or Microsoft Entra domain, or enrolled in an MDM solution, are excluded, and the consumer program "can't be used in commercial scenarios." If you've been told your plant PCs are covered for thirty dollars, check that.
Either way, ESU buys critical and important security updates only. No features, no technical support. It's a bridge, priced to make you cross it.
There's no statistic for this, and it doesn't need one.
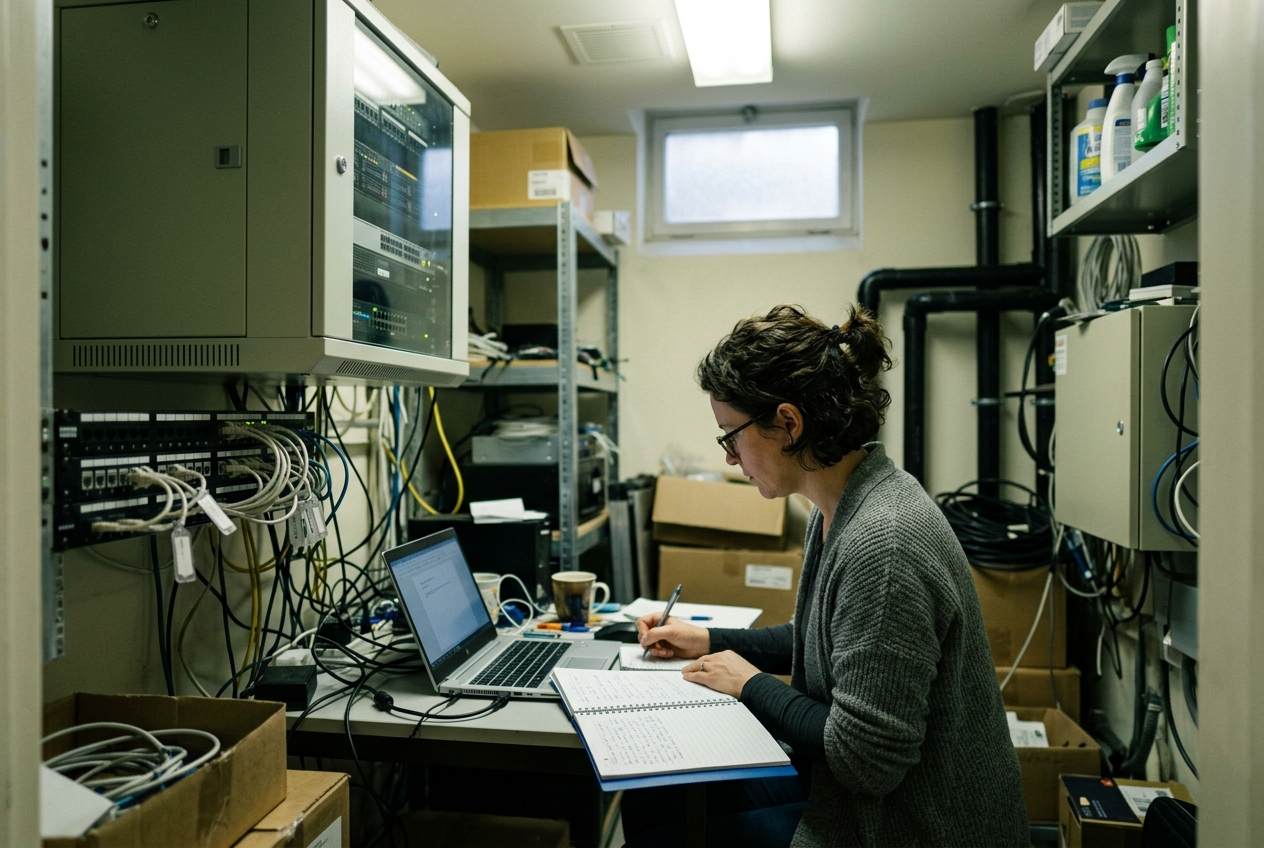
You know whether it's true. There's someone — sometimes titled IT, often not — who knows the VLAN scheme, which switch feeds which cabinet, the login to the firewall, and which machine cannot be rebooted during a run. It lives in their head and in a spreadsheet only they open.
The exposure isn't that they're bad at it. They're usually excellent at it. The exposure is that they take vacations, get sick, and eventually take other jobs, and that none of what they know is written down anywhere you could hand to someone else.
There's a version of this that's easy to miss because it looks like competence: the person is so good at keeping things running that nothing ever escalates to a decision. No one above them has ever had to think about the network, which means no one above them knows what it would cost to replace what's in their head.
The fix isn't replacing them. It's documentation that exists outside one person, and a second set of hands for the nights they're unreachable. If your IT person would be relieved rather than threatened by both of those, that tells you something about whether the current arrangement is working for them either.
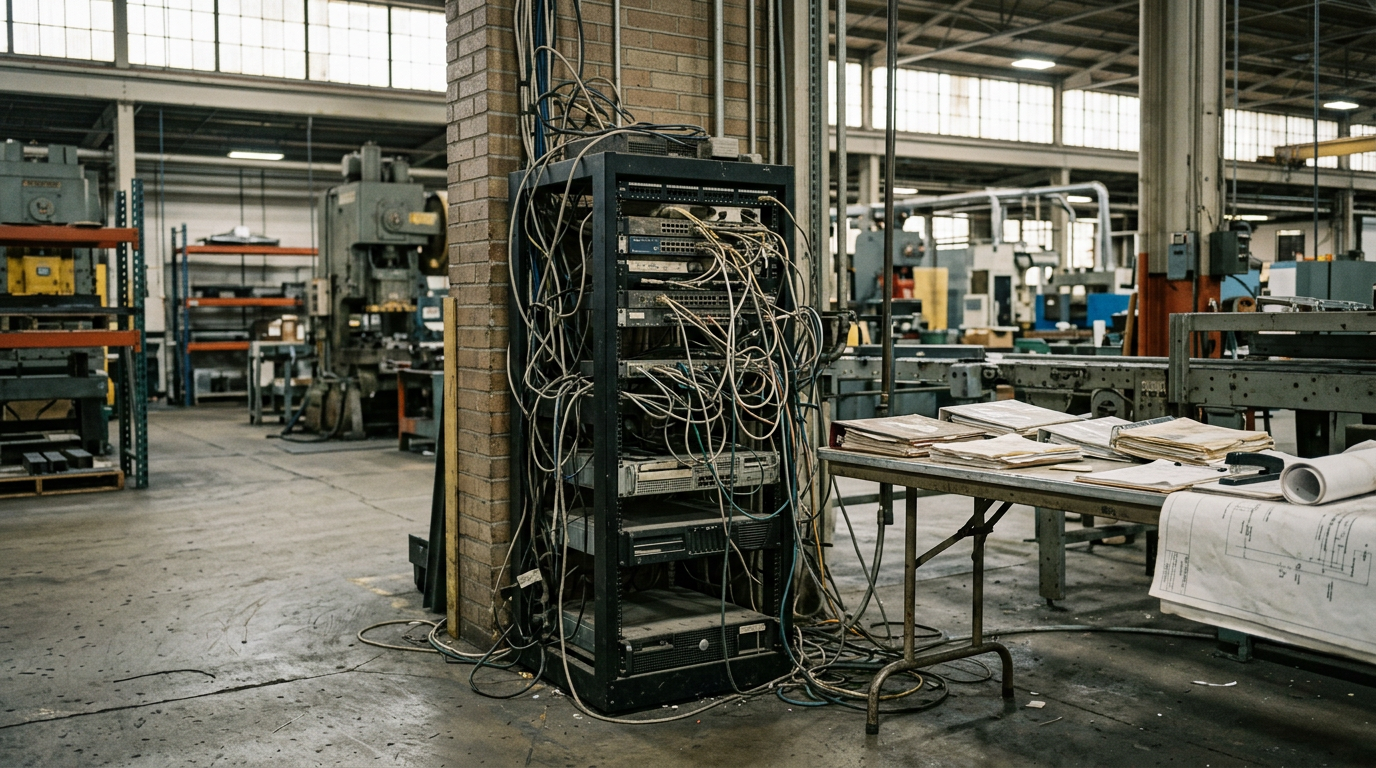
On February 5, 2026, CISA, the FBI, and the UK's National Cyber Security Centre published joint guidance on end-of-support edge devices — load balancers, firewalls, routers, VPN gateways — describing them as a route nation-state actors use to get into networks and stay there.
The companion federal directive is the part worth sitting with. It gives US civilian agencies three months to inventory this equipment and a year to decommission it. The federal government now treats an unsupported firewall as something you're given a deadline to remove, not something to get to next budget cycle.
In most environments this list has never been assembled. The check is concrete: pull your firewall, switch, wireless controller, and VPN appliance models, look up each one's end-of-support date on the manufacturer's site, and see what comes back. It takes an afternoon and the results are usually uncomfortable.
Cyber insurance underwriting has become a control audit. The questionnaire is no longer a formality, and the answers have to be true.
What's actually useful here is that insurers have published which controls their own claims data says matter. Marsh McLennan's Cyber Risk Intelligence Center, in August 2025, matched organizations' self-reported controls against claims outcomes and ranked the five most effective: network hardening, endpoint detection and response, logging and monitoring, security awareness training with phishing testing, and incident response planning.
That's a short, specific list, and it's a reasonable place to start an internal audit — we go through what each one should actually consist of here.
If you can't answer the questionnaire without guessing, that's the sign. Not the premium.
Worth being accurate about the trend, since plenty of content overstates it: this is not primarily a pricing story. Marsh's market reporting has described US cyber insurance rates as softening rather than spiking. What tightened is the underwriting — the scrutiny of what you actually have in place. A renewal that goes through with no questions is a different signal than a renewal that comes back with a control list.
Again, no statistic — the circulating figures on reactive-versus-proactive IT time have no identifiable source, and quoting one would be the same mistake as not planning at all.
The test is simpler. Ask: what's scheduled for the next ninety days? If the honest answer is "whatever breaks," you have a help desk, not an IT function. There's no hardware lifecycle list, no replacement budget, and no one tracking what's aging out.
The consequence isn't dramatic. It's that every equipment decision happens under pressure, at a bad price, with no time to compare options — because it's being made the day something died.
Not "do you have backups." Almost everyone has backups.
When did someone last take a backup, restore it somewhere, and confirm the data came back intact and usable? If the answer is more than twelve months ago, or nobody's sure, then what you have is a backup job that completes successfully, which is a different thing from a backup that works.
This is worth checking precisely because it looks fine on a dashboard right up until the day it doesn't. Backup software reports on whether it finished writing, not on whether what it wrote can be read back into a working system.
There's a second half to the question that gets skipped even more often: how long would a full restore take, and does anyone in operations know that number? A recovery that technically works but takes four days is a different business event than one that takes four hours, and the difference should be agreed with the people who run the floor rather than assumed by whoever owns the backup job.
This is the one that separates a plant, warehouse, or multi-building operation from an office.
The pattern to look for is problems that need someone physically present — a cabinet, a cable run, an access point above racking, a new line that needs drops pulled. None of it resolves over a remote session, and each one stops work for more than one person.
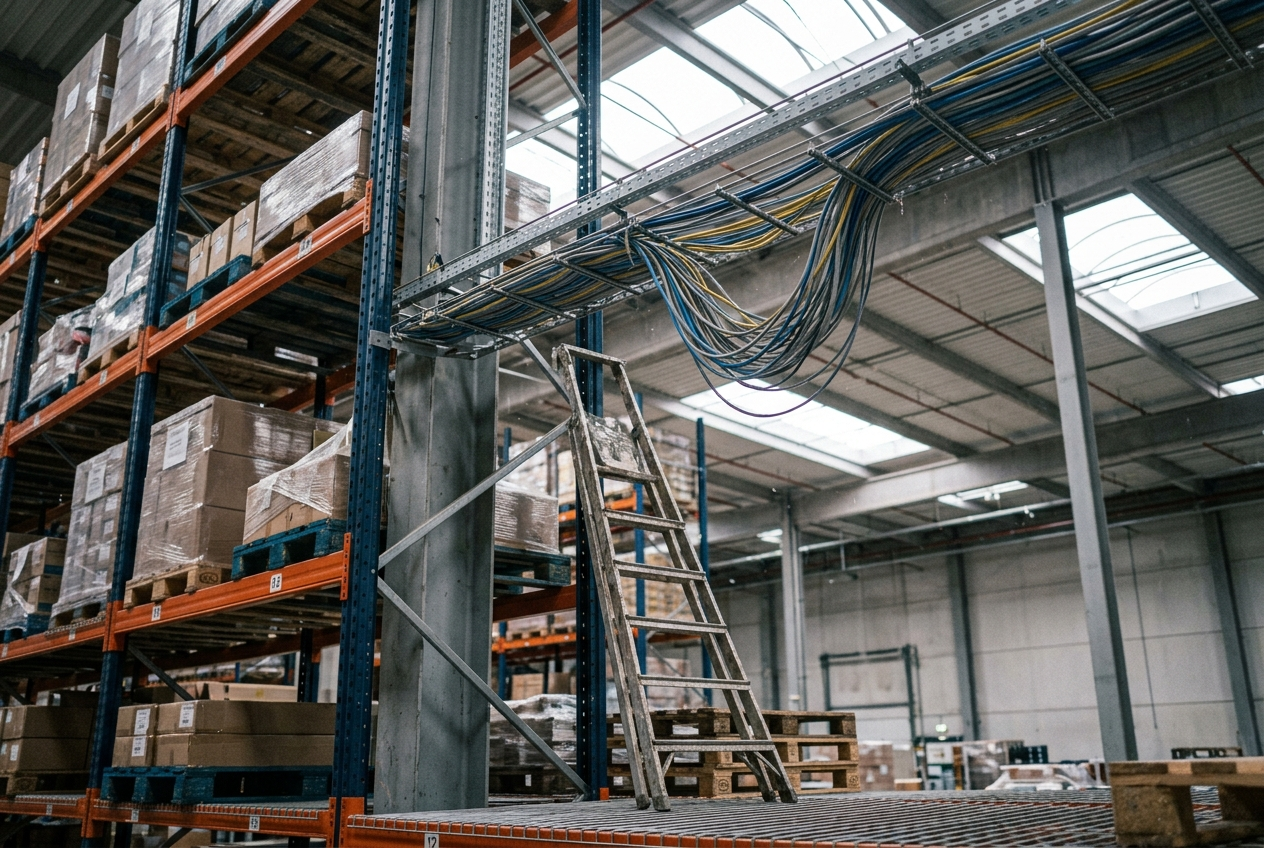
If your current arrangement is a remote-only provider, an internal person who isn't a cable tech, or a break-fix relationship you call after something breaks, you're absorbing that delay every time. We work through how to size your real on-site need here.
The tell is who actually ends up holding the ladder. In a lot of facilities the answer is a maintenance lead or a shift supervisor who took it on because someone had to, and who is now informally responsible for a part of the network nobody assigned them. That works until it doesn't, and it makes the eventual handover harder, because what they know isn't written down either.
There's no clean threshold, and the count matters less than the pattern.
These seven aren't independent. They're symptoms of the same thing — IT being handled by whoever has time rather than by a function with a plan. One of them on its own is a task you can schedule. Several of them together is a structural problem that will keep generating tasks, and clearing them one at a time won't change the rate at which new ones appear.
If you're weighing whether to change the arrangement at all, the more useful comparison is managed IT versus the break-fix model you're probably on now. If you've already decided and you're evaluating providers, here are the ten questions worth asking.
When should a business switch to managed IT services?
There's no headcount threshold. The practical trigger is when IT problems start having business consequences that nobody owns — unplanned downtime, equipment failing without a replacement plan, or an insurance questionnaire you can't answer honestly.
Is Windows 10 still safe to use?
Not without Extended Security Updates. Support ended October 14, 2025, and machines without ESU receive no security patches. Business ESU runs $61 per device for year one and doubles to $122 in year two, which begins November 2026. The cheaper consumer option is not available for business machines — Microsoft excludes devices joined to a domain or enrolled in MDM, and states the consumer program can't be used in commercial scenarios.
How do I know if my network equipment is past end of life?
Pull the model numbers for your firewall, switches, wireless controllers, and VPN appliances, then look up each one's end-of-support date on the manufacturer's site. CISA, the FBI, and the UK NCSC issued joint guidance in February 2026 specifically on the risk of running these devices past support.
Do we need managed IT if we already have an IT person?
Often the arrangement that fits is co-managed rather than fully outsourced — the provider covers what scales badly for a small team, like after-hours coverage and security operations, while your person keeps the work that requires knowing your business. We cover how that split works here.
What does managed IT cost?
It varies enormously with security scope and coverage hours, which is why comparing two monthly numbers is misleading. We break down the benchmark data here.
CTC Technologies supports Michigan businesses from an Ann Arbor headquarters, with technicians who drive to your building.
The first useful step isn't a proposal — it's an inventory. What you're running, what's past support, and where the single points of failure sit. Most of the seven signs above resolve into findings on that one document, which is why it's worth building before anyone quotes you a monthly number.
Request an IT assessment or call 734-408-0200. Managed IT across Michigan, including Detroit, Troy, Warren, Livonia, Sterling Heights, and Ann Arbor.


